
Liability travels where the data goes: your data = your problem
If sensitive information leaves your control, your board holds the blame, even if the breach happened outside your infrastructure.

Most organizations still focus on protecting the perimeter. But data doesn’t stay inside your perimeter. It moves between apps, clouds, partners, and providers, many environments that are outside your control.
And when that data moves unprotected, your liability moves with it.
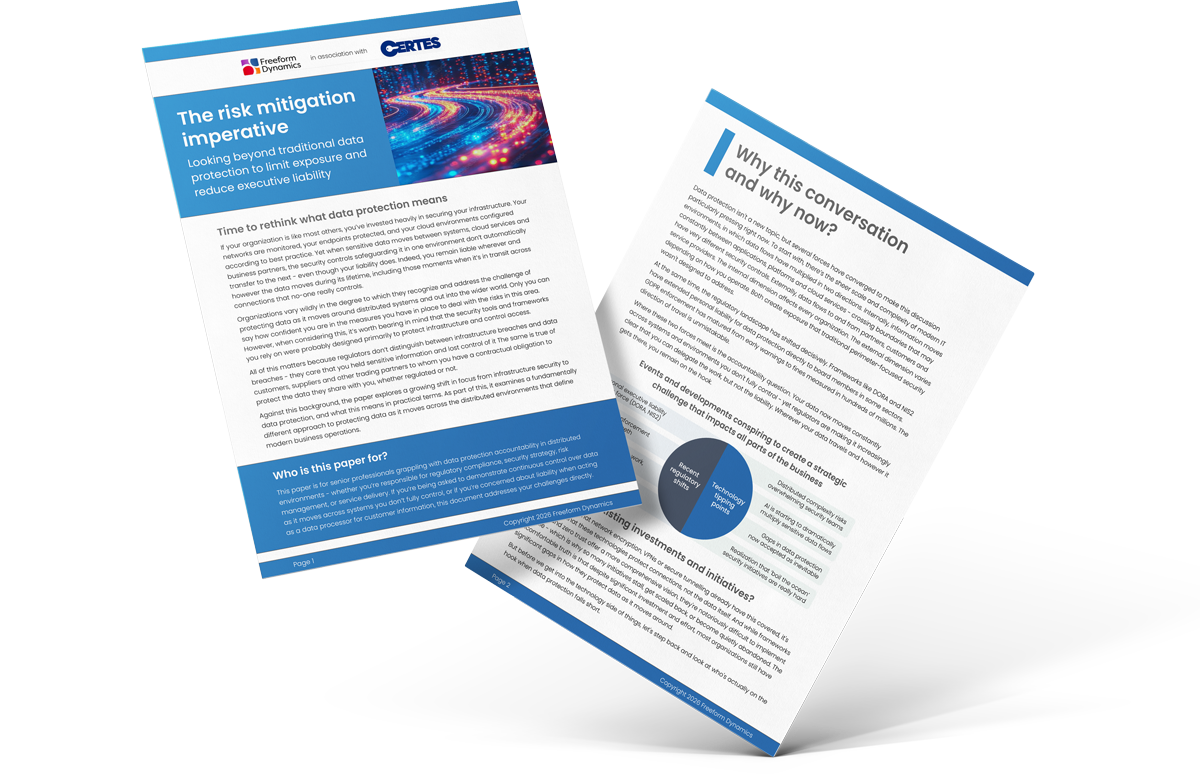
This whitepaper from Certes in partnership with Freeform Dynamics breaks down the critical shift in modern cybersecurity:
You’re no longer judged on how well you defend your systems.
You’re judged on how well you protect your data.
Discover:
- Why infrastructure-first thinking no longer satisfies regulators
- How data-in-motion exposure leads to fines, lawsuits, and board-level risk
- What a data-centric strategy looks like, and how DPRM (Data Protection & Risk Mitigation) ensures compliance, resilience, and post-quantum readiness
Enter your email below to download your FREE white paper
Infrastructure defense doesn’t stop exfiltration.
Firewalls, VPNs, and endpoint agents were designed to keep attackers out. Once an attacker has access, through compromised credentials or third-party connections, your data is exposed, and your compliance is in question. When data moves across systems without persistent protection, you can’t prove control, and that’s exactly what regulators demand.
Certes DPRM protects what legacy tools can’t: the data itself.
Our platform applies persistent, policy-driven protection at Layer 4, ensuring sensitive information stays protected, invisible, and unusable to attackers, even in compromised environments. It’s built to withstand today’s threats and tomorrow’s quantum risks, while delivering the audit-ready evidence compliance teams need.
Most organizations won’t be breached because they lacked firewalls. They’ll be breached because the data was unprotected once attackers got through.
And that’s exactly what regulators, auditors, and legal teams will focus on: was the data protected at every stage, including in transit?
Traditional security tools protect systems. Compliance frameworks demand evidence that you’ve protected the data itself.
Certes DPRM delivers that protection.
By securing data in motion across any network, cloud, or third party, it ensures sensitive information stays protected, inaccessible, and provably under your control, even in compromised environments.
View the whitepaper and see how data-centric protection reduces risk, meets regulatory expectations, and limits breach fallout before it begins.
Frost & Sullivan Recognizes Certes for Post-Quantum Cryptography Leadership: Why Data Protection Can’t Wait
Certes has been awarded Frost & Sullivan’s 2026 Global Enabling Technology Leadership Recognition in Post-Quantum Cryptography, celebrating its innovative approach to protecting sensitive data against emerging quantum threats.

Certes Receives Frost and Sullivan’s 2026 Global Post-Quantum Cryptography Enabling Technology Leadership Recognition
Certes receives Frost & Sullivan's 2026 PQC leadership recognition for quantum-safe data protection, crypto-agility, and securing data without infrastructure changes.
Protect Now, Modernize Over Time: Building Crypto-Agility Around Legacy Systems
Discover how crypto agility for legacy systems enables post-quantum protection for data in transit without costly application rewrites or infrastructure upgrades.